 Open the full preview
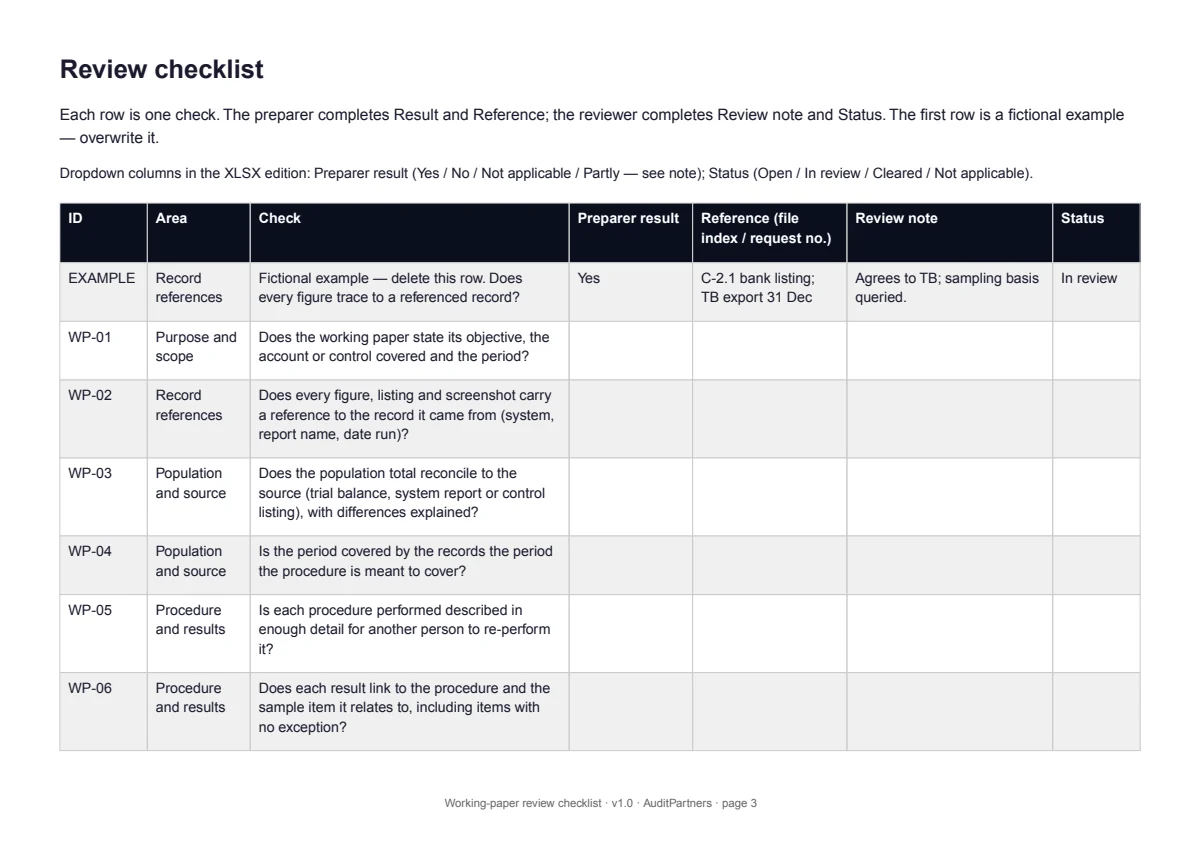
Working-paper review checklist
Check a working paper before sign-off.
Get the free templateAI driven. Human validated.
We focus on the audit work so you can focus more on your clients.
For CPA, SOC and assurance firms. From client records to working papers your reviewers can follow.

Support where your team needs it
Busy season, a new service line or a specialist review: get experienced help with the work holding up your engagement.

Transaction testing and working papers in your audit templates.
Explore this service
Control testing and file preparation for SOC 1 and SOC 2.
Explore this service
Access, change, application and recovery control testing.
Explore this service
Technical support, internal audits and certification preparation.
Explore this service
Governance, permissions and oversight reviews for automated systems.
Explore this service
Extra capacity and specialist skills for your audit plan.
Explore this service
Vendor, privacy, data-use and contract compliance checks.
Explore this serviceFrom records to review
Our professionals prepare and check the work. Your reviewers make the decisions.
Your team shares the request list, templates and client records through the approved channel.
We sort the records, link them to the testing plan and flag anything missing.
We complete the testing sheets and draft working papers in your format.
We identify differences and prepare questions with the supporting records attached.
A qualified audit professional checks the work before your reviewers receive it.
Your reviewers make the judgments, request changes and approve the file.
Your team receives the completed file and resolves any remaining review notes.
Working alongside your firm
Use extra delivery capacity without handing over the relationship you have built.
Our work fits into your templates and review process. A qualified professional checks the file before delivery; your engagement team then asks questions, requests changes and reaches its own conclusions. You stay responsible for the engagement and the report.
Find support for your type of firmAn internal audit, in practice
An ISO/IEC 27001 internal audit for a client preparing for certification.
Our lead auditor worked in a secure, private environment with an AI assistant, directing the work through 79 prompts and reviewing 819 evidence files. The auditor set the scope, challenged the findings and approved the report.
The internal audit was completed and the issues were addressed before the certification audit.
One engagement, reported by the auditor who ran it. The manual figure is our estimate. It shows an AI-assisted workflow with a person in charge, not an automated audit.
Keep your team current
AuditPartners runs staff awareness sessions and leadership workshops. AuditHive™ offers certification training for auditors and IT security professionals through our PECB and EC-Council partnerships.
Explore paths in information security, audit methods, governance, incident response and privacy. Individual learners and company teams can choose the training that fits their roles.
Explore training and certification paths
For enterprise teams
Find out where a control is missing, prepare for an audit or get help putting policies into practice. We review technology risk, information security and compliance requirements, including ISO 27001, ISO 42001, NIST, SOC 2 readiness and CMMC preparation.
We also support IT risk reviews for financial audits, acquisition due diligence and vendor or data-use requirements. Start with the issue your team needs to resolve.
Explore enterprise services
Useful before you engage us
Open the full preview Check a working paper before sign-off.
Get the free template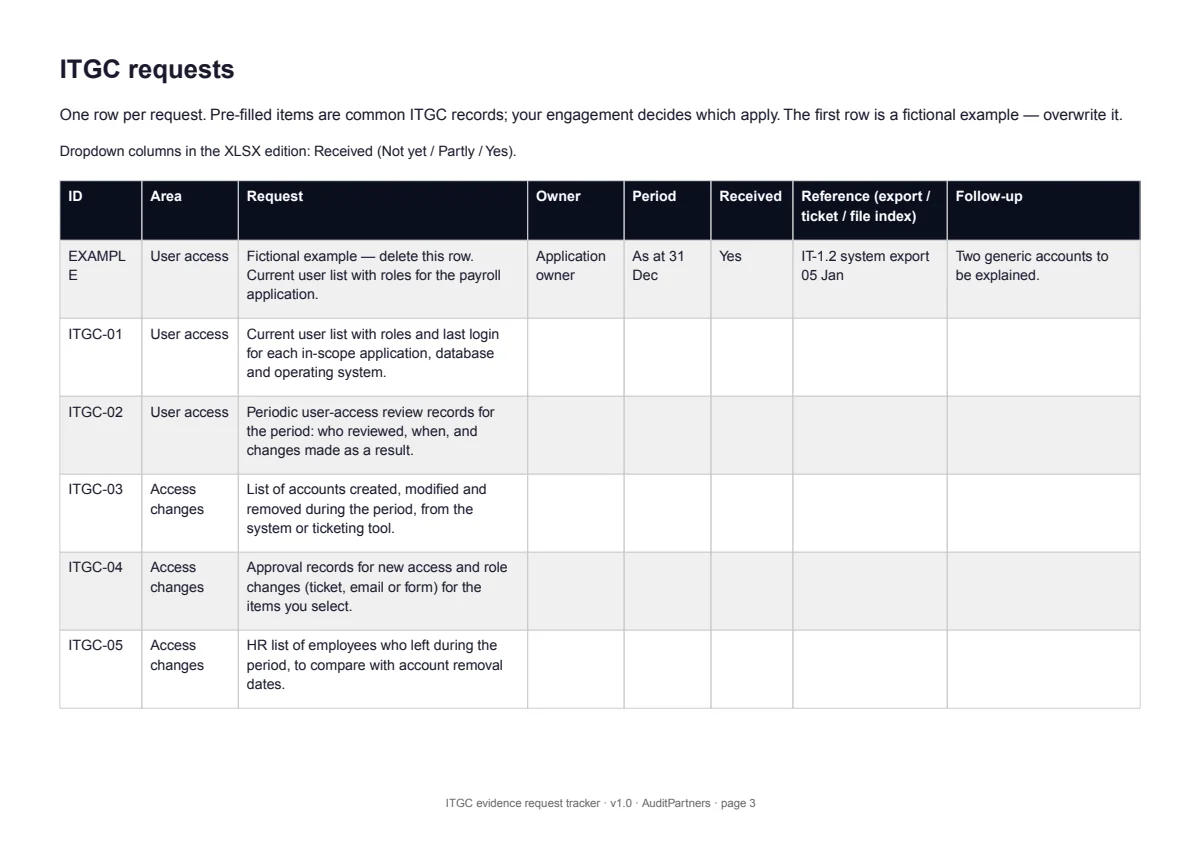 Open the full preview
Keep record requests, owners and follow-up in one file.
Get the free template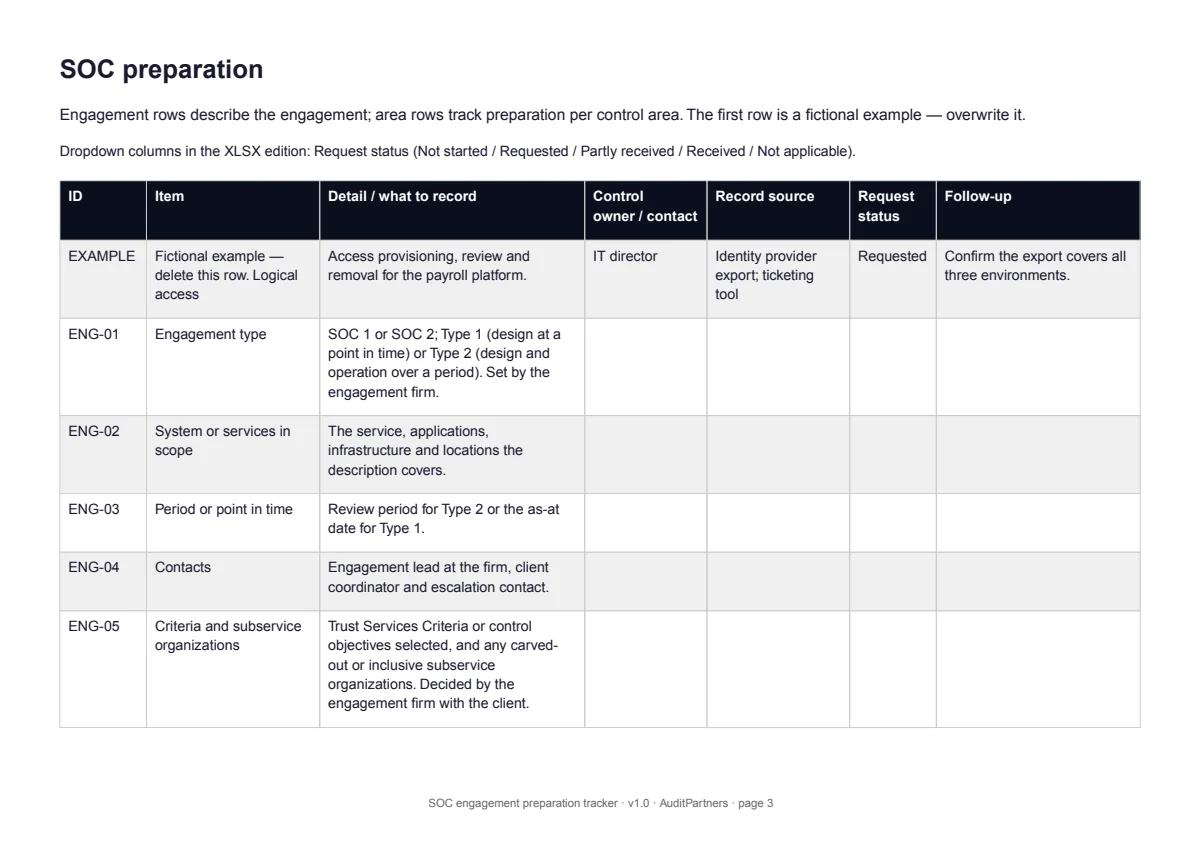 Open the full preview
Prepare contacts, controls and requests for SOC fieldwork.
Get the free templateFeatured guides
Tell us the service, the deadline and the work taking up your team's time. We’ll show you how our team can support an engagement and what your reviewers would receive.
We reply by email within two working days.


